Web3 Daily Exploits — 06 Sep 2026: Reddio ~9.25 ETH Vault Double-Count + Autonolas Gov Attempt
A quiet window produced one confirmed low-value vault exploit and one blocked governance attempt. Reddio’s RedSonic Vault lost approximately 9.25 ETH to a cross-vault double-counting flaw; a malicious Autonolas proposal targeting ~40 ETH remains unexecuted.
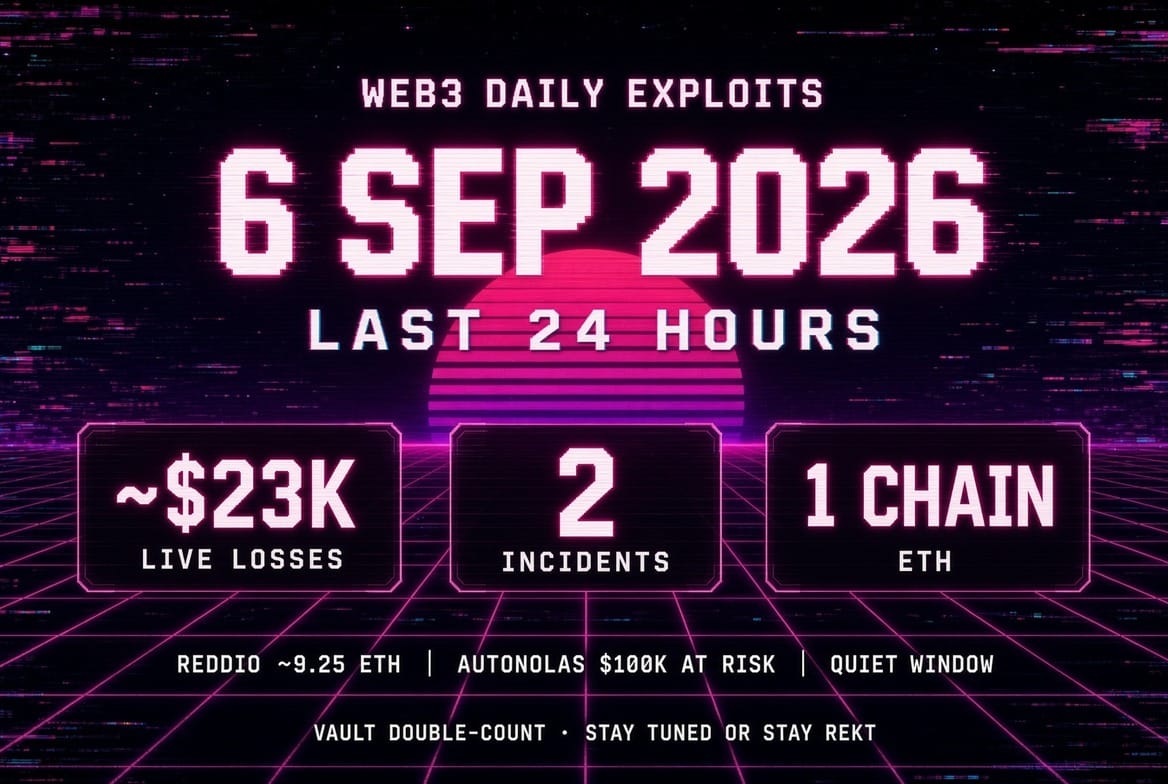
A quiet window produced one confirmed low-value vault exploit and one blocked governance attempt. Reddio’s RedSonic Vault lost approximately 9.25 ETH to a cross-vault double-counting flaw; a malicious Autonolas proposal targeting ~40 ETH remains unexecuted.
Security monitors recorded limited new activity in the past 24 hours. The Reddio incident is confirmed on-chain. The Autonolas proposal has been flagged and the team intends to vote it down. No major bridge, oracle, or high-value protocol drains were newly reported or materially updated in the window. Older incidents such as Notional and Dream Health Chain fall outside the strict 24-hour cutoff and are not re-covered here.
Reddio RedSonic Vault — ~9.25 ETH (Ethereum) — Confirmed
What happened: An attacker drained approximately 9.25 ETH from Reddio’s RedSonic Vault by exploiting a cross-vault asset double-counting vulnerability combined with a flash loan.
Protocol / chain / asset: Reddio (RedSonic Vault / rsvETH) on Ethereum. Assets involved: ETH / WETH and stETH.
Loss: ~9.25 ETH (roughly $23k at contemporaneous prices). No recovery or rollback reported at time of writing.
Attack type: Accounting flaw / permissionless asset registration + shared collateral double-counting + flash-loan price inflation.
Technical details: The ETH vault’s getTotalAssetBalance(ETH) included the raw stETH balance of the vault. Because registerErc20() was permissionless, the attacker registered stETH as a second asset (rsvstETH). The same stETH therefore backed both rsvETH and rsvstETH share classes. Flow (single transaction): flash-loan ~1,139 WETH from Balancer → deposit majority of ETH to control rsvETH shares → register and deposit ~9.34 stETH (inflating rsvETH share price) → redeem inflated rsvETH for excess ETH → redeem rsvstETH to recover the stETH → repay loan. The 2% withdrawal cap did not prevent the share-price manipulation.
Explorer links:
- Attacker: https://etherscan.io/address/0x70f2333d21ed7e7d105f6578227a9a747687982c
- Victim Diamond: https://etherscan.io/address/0x4315990d9eeaffdfafd49958b4851f203fa1126f
- Vulnerable implementation: https://etherscan.io/address/0x92ecc5deacb14937867686ca8b85dd8a65b74704
- Main attack tx: https://etherscan.io/tx/0xe3cba90e865c6cba950ebce36a52607f51f1fd33cd9fb920c78803f19b57791a
Status: Confirmed. Funds moved; no public recovery announcement.
Sources: https://x.com/SlowMist_Team/status/2096439593403089077, https://x.com/exvulsec/status/2096277307757572517
Autonolas Treasury — Malicious Governance Proposal (~40 ETH / ~$100k at risk) — Unexecuted / Flagged
What happened: A Tornado-funded attacker submitted a governance proposal titled “Owner migration: transfer treasury ownership from old timelock to Safe updater.” Execution would have transferred treasury ownership to an attacker-controlled contract, enabling withdrawal of the treasury balance.
Protocol / chain / asset: Autonolas on Ethereum. Treasury holding ~40.196 ETH.
Loss: None realized. ~$100k equivalent still at risk until the proposal is defeated.
Attack type: Malicious governance proposal / social-engineering style ownership transfer.
Technical details: Attacker registered the ENS name “autonolas-deployer.eth” and submitted the proposal. If executed, ownership would move from the legitimate Autonolas Timelock to the attacker contract. Community and monitors have three days to vote it down. Defimon shared the alert in the project’s community chat; the team has indicated it will vote the proposal down.
Status: Unexecuted. Team aware and planning to reject.
Sources: https://x.com/DefimonAlerts/status/2096432367908933790
Also noted
- No additional confirmed high-impact incidents first reported or materially updated in the strict last-24-hour window after cross-checks of DefimonAlerts, SlowMist, CertiKAlert, Phalcon, GoPlus, PeckShield, BlockSec, Lookonchain, and related monitors.
Sources & references
- https://x.com/SlowMist_Team/status/2096439593403089077
- https://x.com/exvulsec/status/2096277307757572517
- https://x.com/DefimonAlerts/status/2096432367908933790
- https://etherscan.io/tx/0xe3cba90e865c6cba950ebce36a52607f51f1fd33cd9fb920c78803f19b57791a
Editor’s note: Quiet day. All figures are live losses after any known reversals; no how-to details are included. Always verify on-chain before acting on alerts.
Read more
Web3 Daily Exploits — 23 Oct 2026: WAX ~$90.5K Bridge Negative Fee Zero Debit
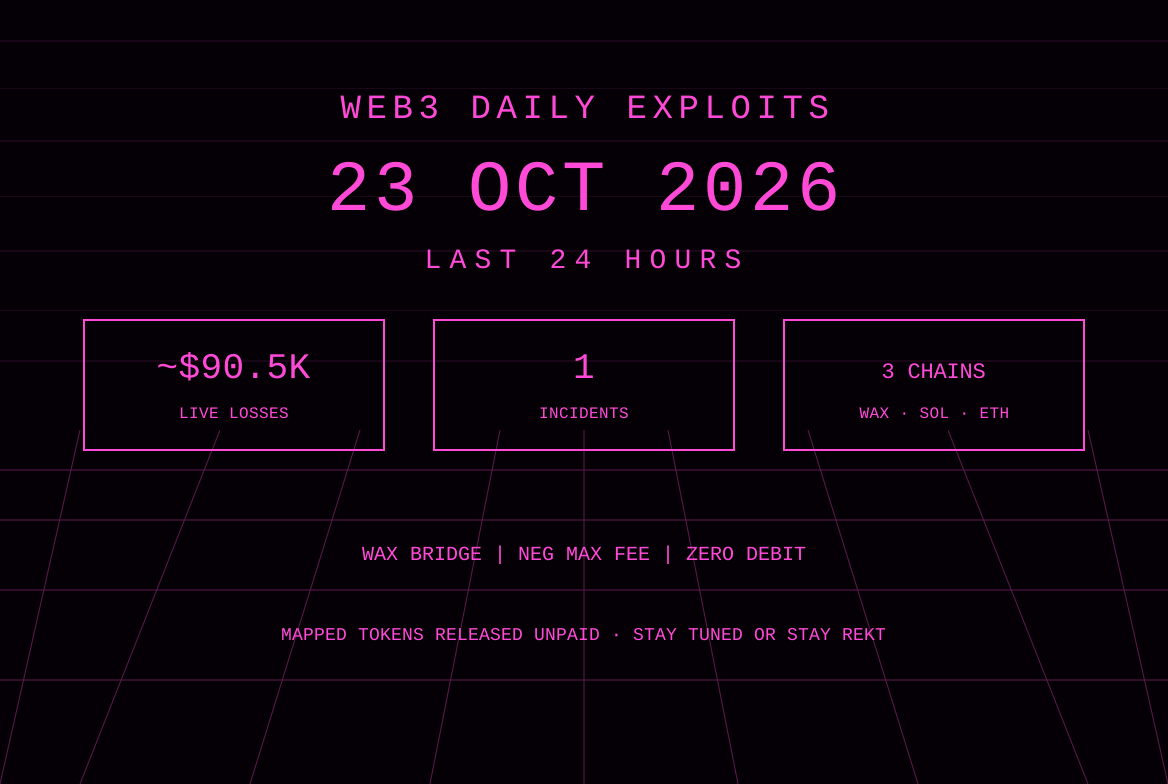
WAX Multi-Chain Bridge drained ~$90.5K after eth.token::withdraw allowed negative max_fee that zeroed the debit while still logging full withdrawals and releasing mapped USDC/USDT/DAI/WETH/WBTC on Solana and Ethereum. SlowMist and Blockaid first reports. Live loss ~$0.09M, 1 incident, 3 chains. Kimchi Solana KOL pump-dump and CoinDCX wallet movements noted as UPDATE.
Web3 Daily Exploits — 22 Oct 2026: NEM ~$820K LP Burn Reserve Manip
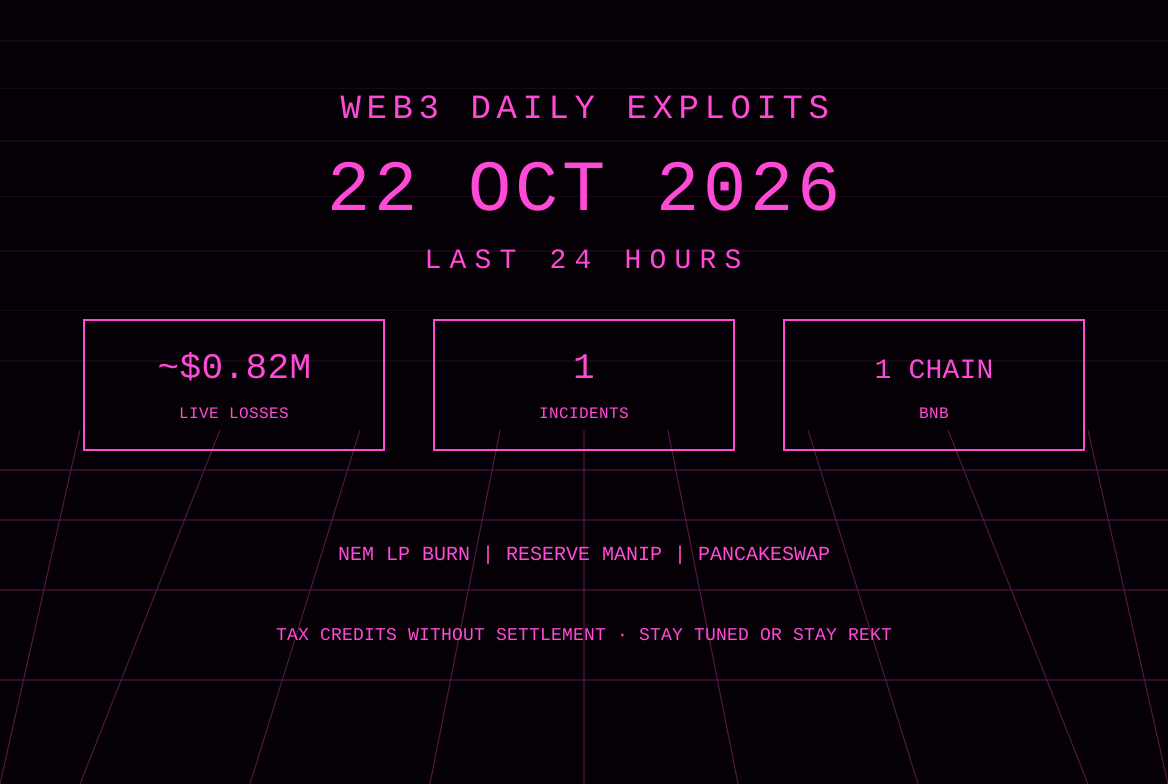
NEM (Newmont) token on BNB Chain drained ~$820K from its PancakeSwap USDT/NEM LP after a tax-settlement flaw let the attacker inflate pendingLpSellRecycle without real sells, then burn existing reserves via flushLpSellRecycle + sync. Defimon, CertiK, SlowMist, Phalcon first reports. Live loss ~$0.82M, 1 incident, 1 chain. Cysic bounty and Fearless Wallet key-leak noted as UPDATE.
Web3 Daily Exploits — 21 Oct 2026: Slice ~$41K FundsModule Unbacked Release + MORPHO ~$2.3M EIP-7702 Drain
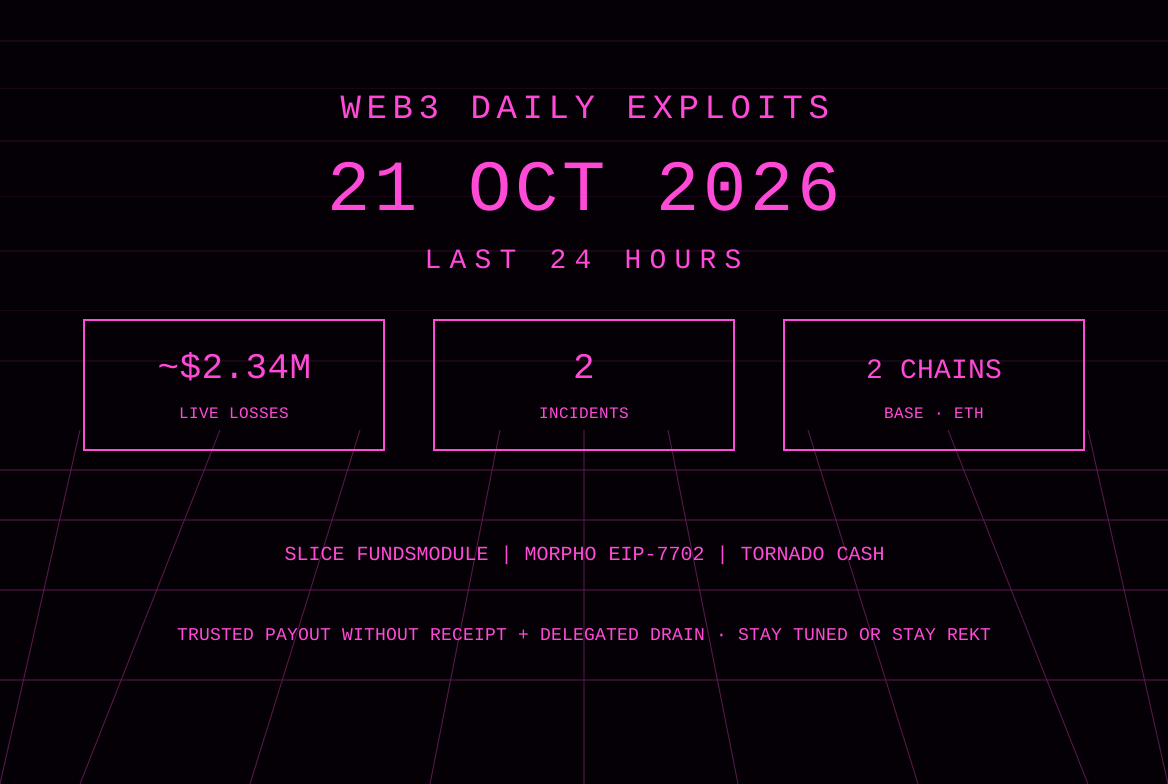
Slice FundsModule on Base drained for ~$41K after release function trusted caller-selected source contracts without verifying actual ETH or USDC receipt. Institutional addresses lost ~973K MORPHO (~$2.3M) via EIP-7702 delegations, funds to Tornado Cash. SlowMist and Defimon first reports on Slice; ZachXBT on MORPHO. Live loss ~$2.34M, 2 incidents, 2 chains. Drift fund movements noted as UPDATE.
Web3 Daily Exploits — 20 Oct 2026: Argent-Style Wallet ~$60K Recovery Deadline Wrap + Payload Replay
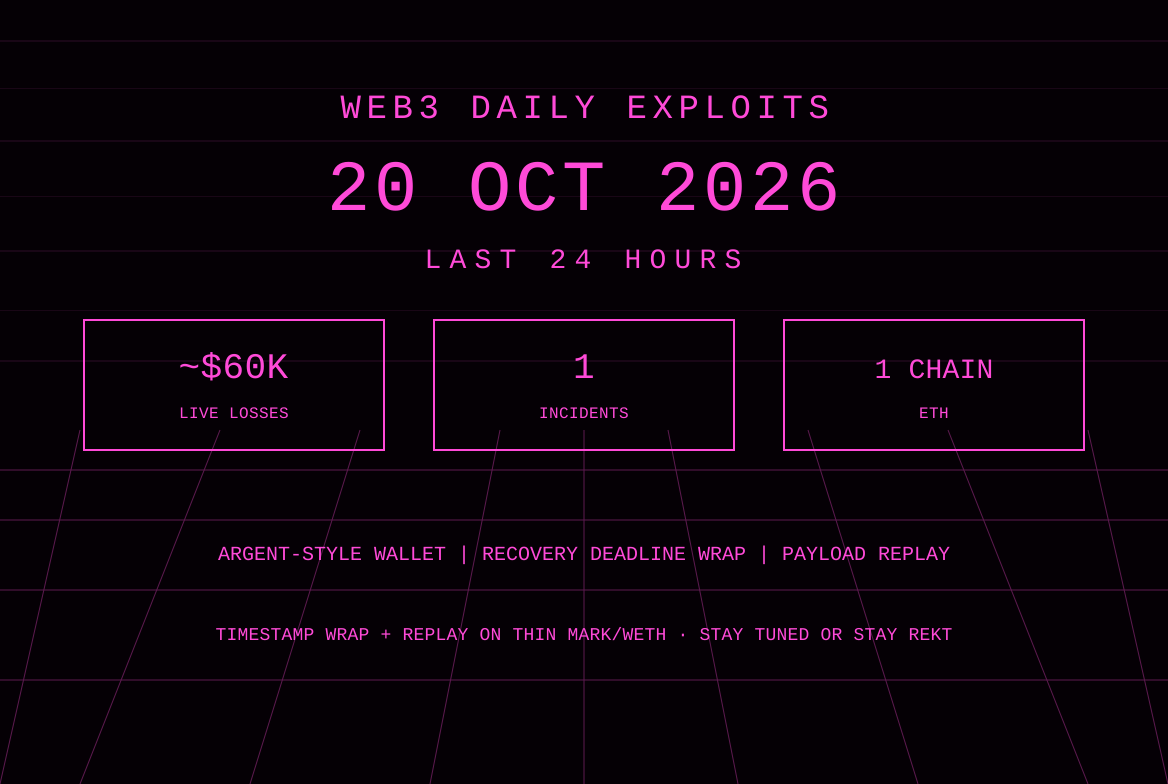
Argent-style smart wallet system on Ethereum drained for ~$59.8K after unrestricted recovery-period setter caused deadline wrap to past timestamp and execution module allowed signed payload reuse, used against thin MARK/WETH pool. SlowMist first report. Live loss ~$60K, 1 incident, 1 chain. Drift and Aztec fund movements noted as UPDATE.